A Developer's Guide to Securing Your Web Application in 2024

Security by Design

In an era of sophisticated cyber threats and stringent data protection regulations (including the Kenya Data Protection Act), application security cannot be an afterthought - it must be woven into every line of code from day one.

Critical Security Layers

Input Sanitization & Parameterized Queries: Never trust raw client input. Utilize prepared statements and robust ORMs to eliminate SQL Injection (SQLi) vulnerabilities entirely.

Cryptographic CSRF Tokens: Protect state-changing operations by enforcing unique, cryptographically signed anti-forgery tokens on every HTTP POST and PUT request.

Strict Content Security Policy (CSP): Implement modern CSP, X-Frame-Options, and Strict-Transport-Security (HSTS) headers.

Share this insight: Help colleagues & founders discover this article
Related Articles

Why Custom Software Beats Off-the-Shelf Solutions Every Time
Software Development Jul 15, 2024

Why Custom Software Beats Off-the-Shelf Solutions Every Time

Discover why investing in custom software development gives your business a competitive edge over generic, one-size-fits-all solutions in modern African markets.

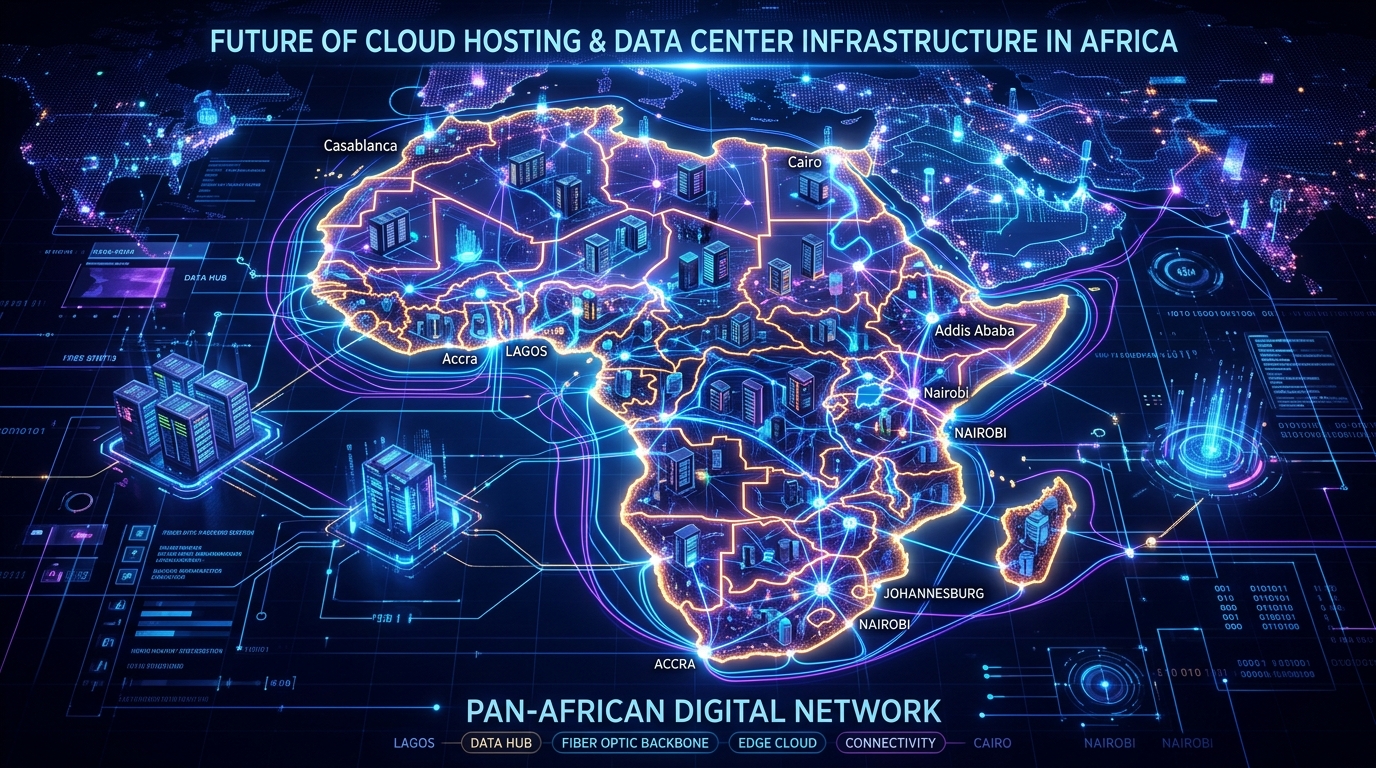
The Future of Cloud Hosting in Africa: Trends and Opportunities
Cloud & Infrastructure Jun 28, 2024

The Future of Cloud Hosting in Africa: Trends and Opportunities

Exploring the rapidly evolving cloud infrastructure landscape in Africa and what it means for businesses looking to scale digitally with high availability.

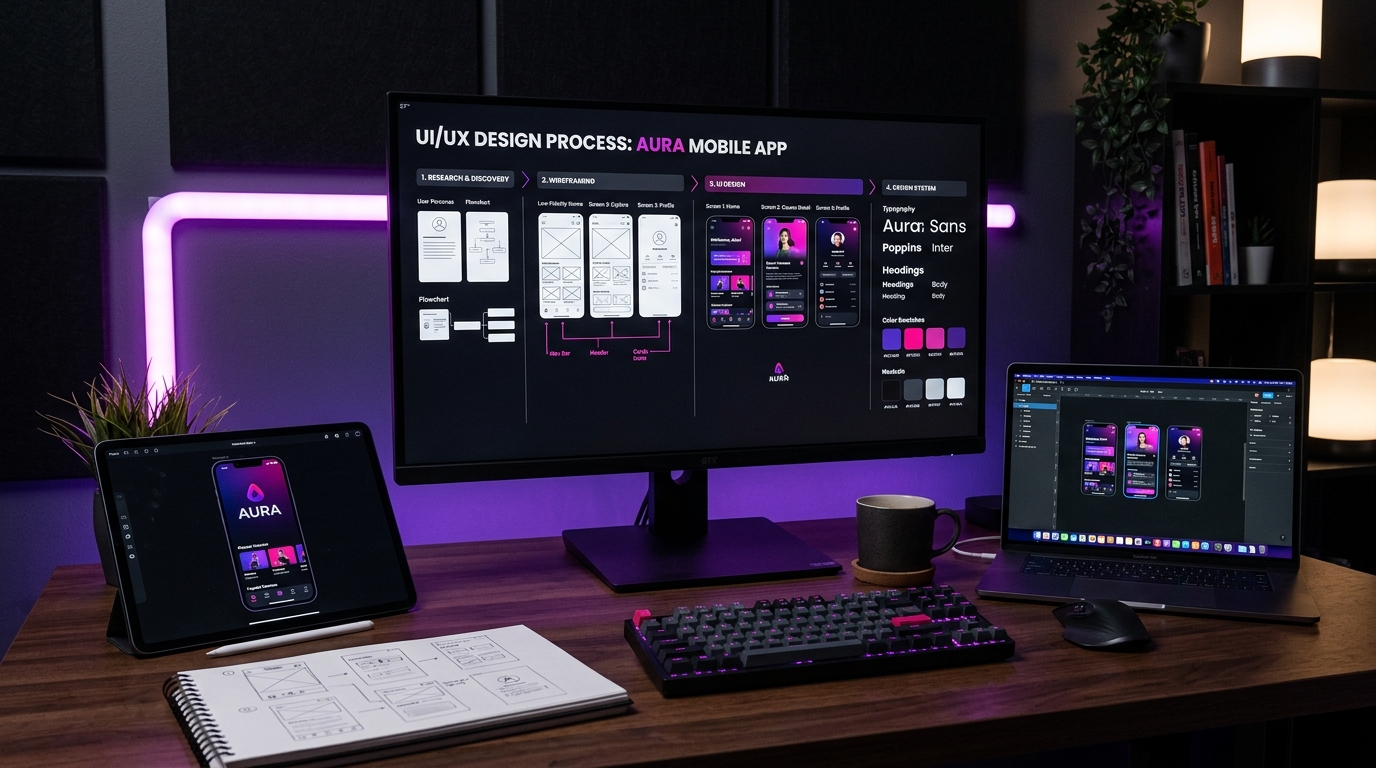
7 UI/UX Design Principles That Actually Convert Visitors to Customers
Product Design Jun 10, 2024

7 UI/UX Design Principles That Actually Convert Visitors to Customers

Learn the core product design principles that transform good websites into high-converting revenue drivers - backed by data and user behavior psychology.